ESSENTIAL
Account and device protection, safer authentication, updates, home-network basics, backup readiness and understandable recovery.
APDD INTRODUCES CIPHERFALL
We don't ask you to trust the word “secure.” We test what the security actually does.
CipherFall is APDD's developing cybersecurity capability. It examines not only whether protection exists, but whether it operates as intended, what it depends on, what happens when conditions change, and whether recovery can be trusted again.

CIPHERFALL — THE FORTRESS OF EVIDENCE
SECURITY + SPEED
Protection that is strong but too slow to detect, understand, contain, or recover from a material change can still leave what matters exposed. CipherFall examines security and response together: what is protected, how quickly consequential change becomes visible, whether the evidence can be trusted, which dependencies are involved, and whether action can occur without creating another weakness.
Speed does not mean acting recklessly. A fast response based on bad evidence can make a security event worse. CipherFall therefore treats response speed and decision quality as connected requirements. The objective is timely, evidence-bounded action: detect meaningful change, establish what can actually be known, contain consequences when appropriate, preserve evidence, and support trustworthy recovery.
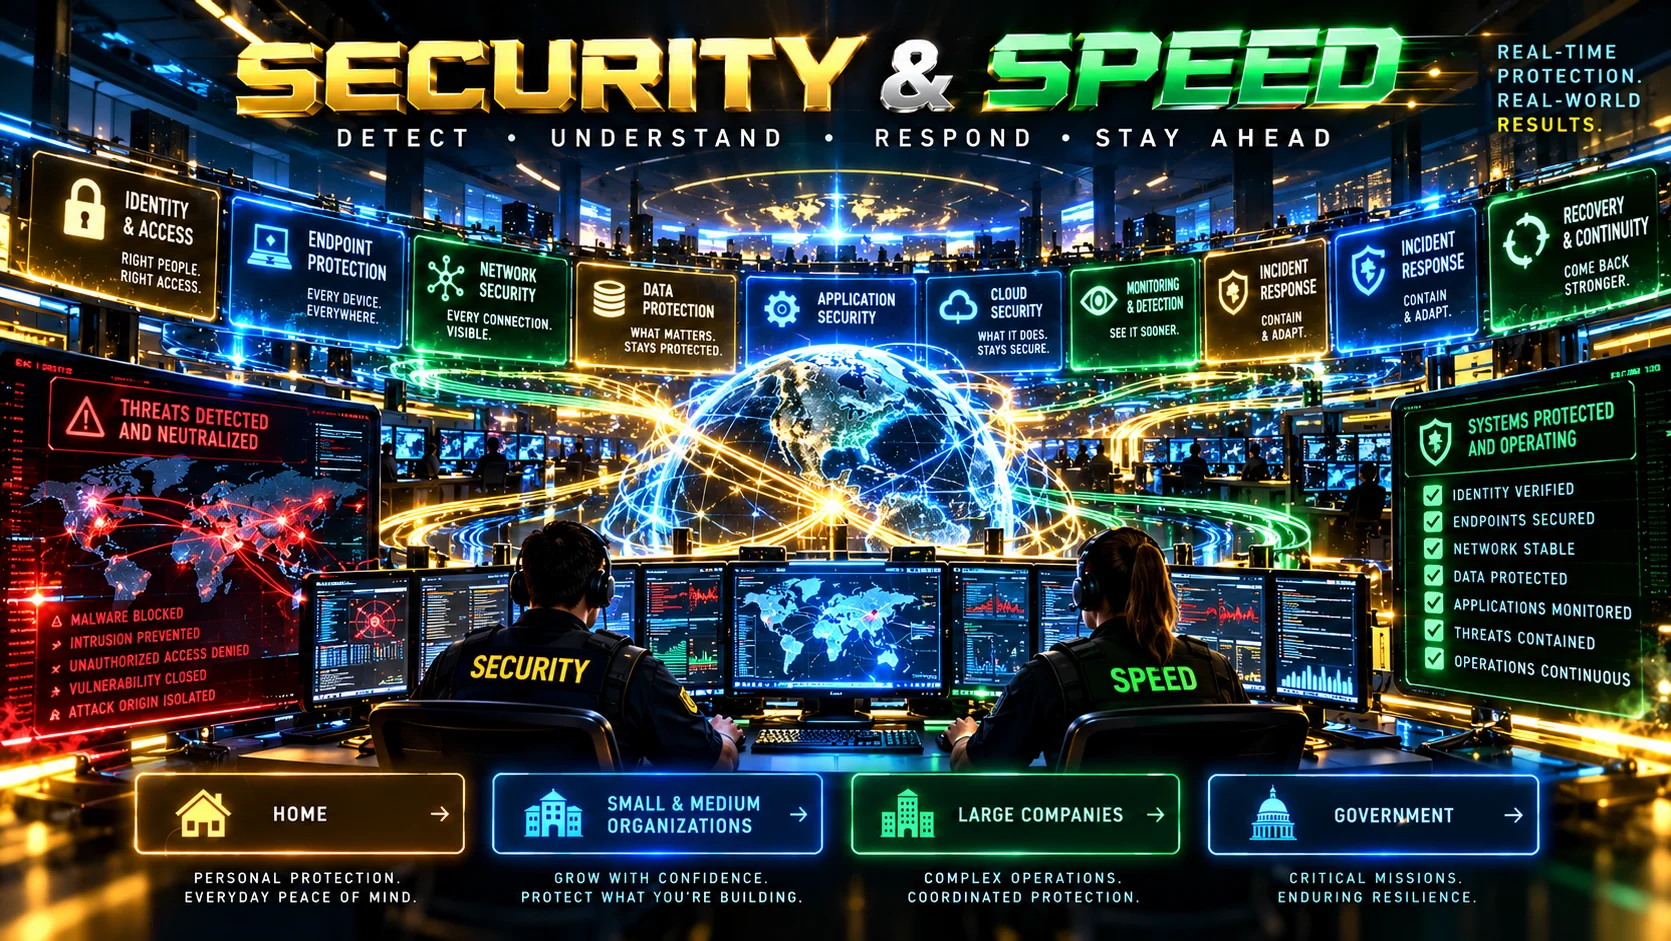
SECURITY + SPEED — protection must remain effective while conditions are changing.
ONE CAPABILITY · DIFFERENT OPERATING REALITIES
A household, a growing organization, a large enterprise, and a government mission do not carry the same identities, devices, data, dependencies, staffing, recovery requirements, or consequences of failure. CipherFall therefore treats protection as an environment-specific evidence problem—not a one-size-fits-all checklist.
01 · HOME
Home protection must cover people, accounts, devices, personal data, networks, backups and recovery without becoming so complicated that the protection is abandoned.
Account and device protection, safer authentication, updates, home-network basics, backup readiness and understandable recovery.
Stronger identity controls, device and network visibility, improved data protection, recovery verification and awareness when important conditions change.
Expanded monitoring, dependency awareness, stronger isolation and recovery controls, and deeper verification for households with higher consequence or exposure.
02 · SMALL & MEDIUM ORGANIZATIONS
The job is to protect people, operations, cloud services, endpoints, business data, vendors and recovery while keeping the system operable by the organization that actually has to run it.
Identity, endpoints, cloud and SaaS, business data, essential visibility, backup and recovery fundamentals.
Stronger access policy, segmentation, evidence and telemetry, vendor/dependency awareness, containment and verified recovery.
Deeper continuous assurance, change awareness, cross-system interaction testing, stronger recovery validation and independent failure paths where evidence justifies them.
03 · LARGE COMPANIES
Large environments add distributed authority, applications, infrastructure, suppliers, data flows, security teams, policy layers and shared services. Local success does not automatically mean the whole remains healthy.
Governed identity, endpoints, applications, data, networks, telemetry, response and recovery across the operating environment.
Stronger policy and enforcement separation, dependency/failure-domain mapping, supply-chain provenance, continuous assurance and cross-system testing.
Higher-consequence containment, independence testing, recovery provenance, evidence freshness, change-causality and reproducible assurance.
04 · GOVERNMENT
Government protection must be driven by mission consequence and the requirements that actually apply to the system. CipherFall's government work is being developed around traceable implementation, persistent evidence, challenge, recovery, change and honest uncertainty.
Applicable public requirements mapped to implementation, evidence and identified gaps rather than assumed from design intent.
Persistent evidence, continuous monitoring, independent verification where applicable, and stronger dependency, recovery and change testing.
Deeper mission-consequence, correlated-failure, recovery, evidence-integrity and operational-reality testing, subject to applicable authority and requirements.
PROTECTION ACROSS EVERY ENVIRONMENT
The operating environment changes, but the discipline does not: understand what matters, establish what the protection depends on, test the relationships that can change the outcome, expose uncertainty, and preserve evidence when reality disagrees with the expected result.

CIPHERFALL PROTECTION ACROSS ENVIRONMENTS — conceptual visualization. Any interface indicators shown are illustrative and do not represent measured performance or certification.
WHERE STRONG PROTECTION CAN STILL BREAK
One constrained component can determine the real strength of several otherwise capable protections.
A control may quietly depend on another identity, service, policy, source or decision being correct.
Two defenses can look independent while failing together because they share the same underlying dependency.
Protection that cannot be maintained correctly under real staffing, workload and change may weaken despite sound design.
Restoring operation does not by itself establish that the restored state is trustworthy.
Missing, stale or contradictory evidence should reduce confidence rather than disappear behind a green status indicator.
A passing control or test can still leave the mission exposed if the test did not measure the consequential condition.
Legitimate controls can create new behavior when they interact. The relationship itself may require testing.
WHEN PROTECTION IS CHALLENGED
Prevention is only part of cybersecurity. When an event suggests that protection may have been bypassed—or the available evidence can no longer establish that it held—CipherFall shifts the question from assumption to investigation: what happened, what was affected, what must be contained, what evidence must be preserved, and what would be required to trust the environment again?

SECURITY + SPEED — when protection is challenged, timely response must still be guided by trustworthy evidence.
WHEN TRUST CANNOT BE ESTABLISHED
Missing or contradictory evidence is not converted into confidence. When required trust cannot be established, the affected conclusion should be degraded or withheld, the evidence preserved, the condition investigated, and recovery or correction re-verified before confidence returns.
REDUNDANT ≠ INDEPENDENT.
RESTORED ≠ TRUSTWORTHY.
MONITORED ≠ UNDERSTOOD.
COMPLIANT ≠ EMPIRICALLY EFFECTIVE.
HOW APDD CHALLENGES CIPHERFALL
Within authorized and controlled scopes, CipherFall is challenged through failure testing, adversarial review, dependency challenges, recovery tests, change tests, false-success tests and retesting. A passing test establishes only what that test actually demonstrated.
A failure is not hidden to protect a preferred conclusion. It becomes information about the protection, the test, the assumptions or the relationships surrounding them.
Changing the system is not the end of correction. The corrected condition must be tested again, including adjacent consequences where they matter.
A material change in software, policy, dependency, identity, evidence or operating conditions can invalidate what earlier evidence established.
When evidence cannot establish a conclusion, UNKNOWN is a legitimate state. Confidence should not outrun what can be demonstrated.
CURRENT EVIDENCE BOUNDARY
Current CipherFall work includes evidence-controlled defensive architecture and controlled local-model testing of selected integrity, dependency, recovery, change and assurance principles. That work is meaningful—but its scope matters.
As evidence grows, claims may grow. If later evidence weakens a conclusion, the claim should shrink. Reality keeps voting.
CYBERSECURITY PROTECTION THAT CAN BE EXAMINED
Modern cybersecurity protection spans identity and access, endpoint protection, network security, application security, data protection, cloud services, monitoring and detection, incident response, business continuity, backup, and recovery. Each area can contain capable controls and still depend on another service, policy, person, device, source of evidence, or recovery path. CipherFall is being developed to examine those relationships as part of the protection itself.
That matters because a security control can perform its local job while the larger operating environment remains exposed. An authentication system may be strong while account recovery is weak. Two monitoring paths may appear redundant while sharing the same underlying service. A backup can restore data while also restoring an unwanted condition. A security dashboard can remain green while required evidence has become stale. CipherFall treats these possibilities as questions to investigate rather than assumptions to ignore.
Prevention remains important, but cybersecurity cannot depend on prevention always succeeding. Resilience also requires the ability to detect consequential change, understand what evidence is available, contain effects where appropriate, recover operation, and establish whether the recovered state can be trusted. The recovery process therefore belongs inside the security problem rather than after it.
CipherFall also distinguishes redundancy from independence. Multiple controls can improve resilience, but simply having two of something does not establish that they will survive the same failure. Shared infrastructure, shared credentials, shared policy, shared software, shared evidence sources, or shared operational assumptions can create correlated failure. The relationship between protections may matter as much as the protections viewed separately.
Identity protection is not only a login problem. Organizations need to understand who or what is requesting access, what authority is actually granted, which policy permits the action, where enforcement occurs, what evidence records the decision, and what happens when identity or authority changes. CipherFall's developing approach treats those relationships as a chain that can be examined for gaps, inherited trust, stale state and unintended authority.
For households, that may mean making account protection and recovery understandable enough to use consistently. For a small or medium organization, it can mean reducing the chance that one compromised account, vendor, device, or cloud service quietly expands into a larger business problem. Large companies add distributed identities, applications, suppliers, data flows and policy layers. Government environments can add formal requirements, mission consequences, persistent evidence and independent assessment obligations. The underlying question remains consistent: what does this protection depend on, and what happens when that dependency is wrong or unavailable?
Cybersecurity monitoring produces events, alerts, logs and status indicators. More telemetry does not automatically create more understanding. CipherFall is being developed around the idea that evidence should have provenance, relevance and freshness appropriate to the conclusion being made. Missing or contradictory evidence should be visible. A system should not silently turn uncertainty into confidence simply because a dashboard needs a status.
This evidence discipline also affects incident response. Fast action can be valuable, but action based on a false conclusion can increase operational damage. CipherFall therefore connects detection, decision quality, containment, authority, evidence preservation and recovery. The goal is not maximum activity. The goal is an appropriate response supported by what can actually be established at that moment.
Business continuity and disaster recovery are essential parts of cybersecurity because an organization eventually has to trust a restored system enough to operate it. CipherFall asks additional questions around recovery: Where did the restored state come from? Is the recovery source current enough? Was its integrity established? Did the restoration reproduce the condition that caused the problem? Have identity, policy, dependencies and evidence been re-evaluated after restoration? What evidence justifies returning the affected capability to normal operation?
Those questions apply differently across the four CipherFall environments. A home user needs practical recovery that does not require a security operations center. A small organization needs reliable recovery without an unrealistic staffing burden. A large enterprise must consider distributed systems and correlated dependencies. A government system must also satisfy the requirements and authorities applicable to its mission. CipherFall does not assume one recovery design fits all four.

OPERATIONAL ASSURANCE CONCEPT — interface values shown in this visualization are illustrative and are not measured CipherFall performance results.
Cybersecurity is not static. Software changes. Accounts change. Policies change. Vendors change. Infrastructure changes. Threat conditions change. A conclusion supported yesterday may no longer be supported after a material change. CipherFall is therefore being developed to treat evidence as something that can expire or require renewed verification when important assumptions change.
Continuous assurance does not mean performing meaningless tests every minute simply to claim continuous security. The cadence should reflect consequence, change velocity, evidence freshness, tolerated detection delay, operational cost and the quality of the test itself. Some conditions justify immediate challenge when an event occurs. Others are better examined periodically or through deeper scheduled testing. The point is to keep assurance connected to reality instead of to a ceremonial testing calendar.
A protection that is technically sophisticated but routinely bypassed, misconfigured, ignored or disabled because people cannot sustain it has an operational weakness. CipherFall therefore treats usability, staffing, performance, privacy, availability, maintenance and recovery burden as part of security evaluation. This is particularly important for homes and smaller organizations, but large enterprises and government programs face the same principle at greater scale.
Adding another control is not automatically an improvement. Every additional mechanism can introduce dependencies, complexity, maintenance, false positives, performance cost or new failure modes. APDD's approach is to ask whether an added protection contributes unique, measurable value and whether that value survives testing, change and recovery. Where simpler protection produces the same or better result with fewer dependencies, simplification deserves consideration.
CipherFall is being developed toward cybersecurity protection whose claims can be traced to evidence: what was tested, under what conditions, what failed, what was corrected, what was retested, what remains uncertain, and what changes would require the conclusion to be examined again. Controlled local-model evidence is only one stage of that work. Broader operational, comparative and independent evidence must be earned before broader claims can responsibly be made.
This is why the public CipherFall page states its current limits. APDD is not using the existence of an architecture, a successful demonstration, a compliance reference, or a passing test as permission to claim universal security. The intended direction is stronger: make the protection understandable, make important relationships visible, challenge the protection itself, preserve failures as evidence, and allow the claim to grow—or shrink—according to what reality demonstrates.
THE CIPHERFALL STANDARD
WE DON'T ASK YOU TO TRUST THE WORD “SECURE.”
WE TEST WHAT THE SECURITY ACTUALLY DOES.
REALITY KEEPS VOTING.
EVIDENCE DECIDES.